PTIR — Daily Briefing — November 22, 2026
by
Executive Summary
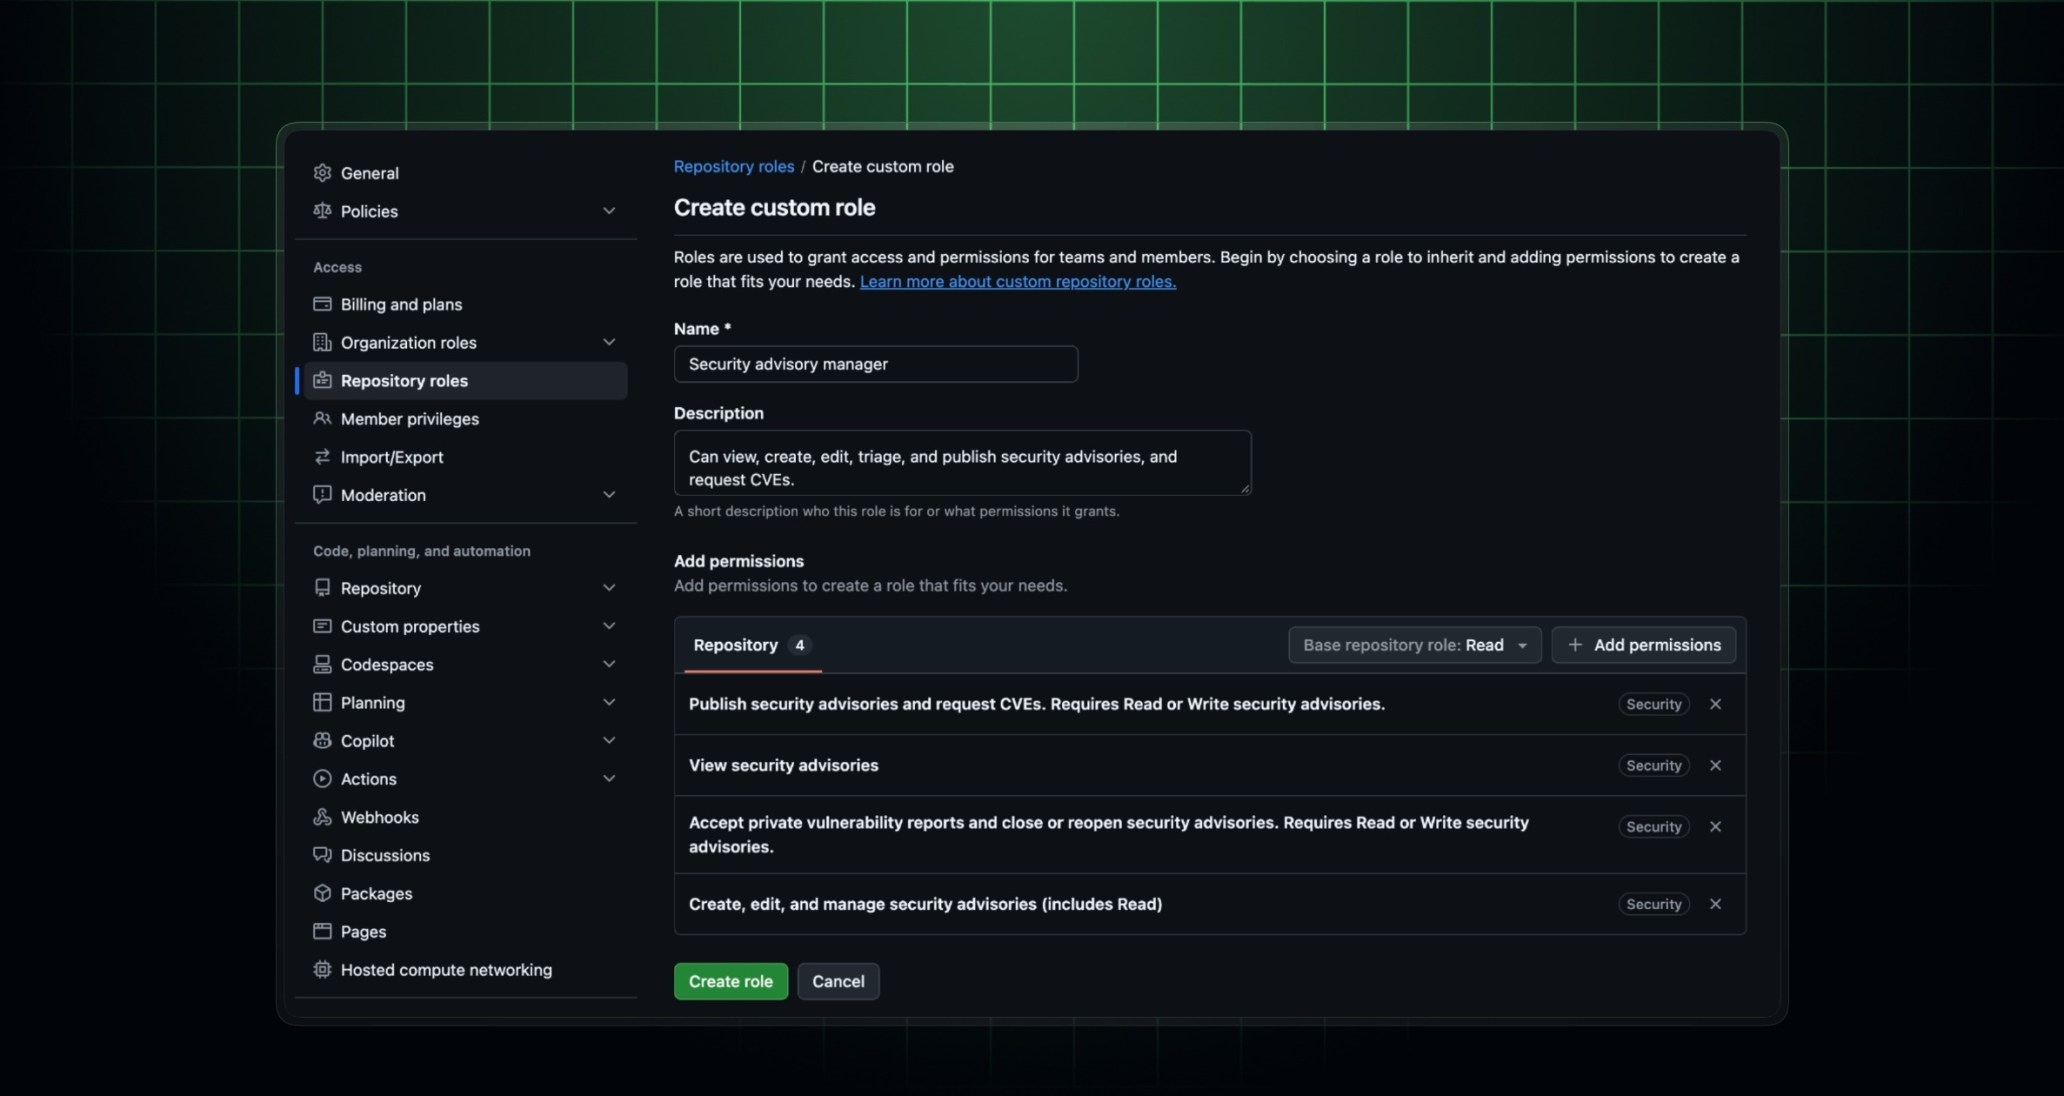
A new Fedora Linux 45 lab offers a careful, reproducible model for testing FIDO2 security keys across encrypted-disk unlock, desktop login, sudo, polkit, and SSH—while documenting failures and preserving password recovery. GitHub has also made security-advisory permissions generally available through custom repository roles, allowing organizations to delegate private vulnerability work without granting repository-administrator access.
Action Queue
1. Read the Fedora FIDO2 lab before experimenting with security-key login
The Fedora Linux 45 guide is valuable less as a copy-and-paste recipe than as an example of responsible systems testing. It distinguishes LUKS enrollment from PAM registration, keeps password fallback, requires two keys and recovery media, and reports that two Identiv uTrust devices were unreliable for boot unlocking on the test machine.
- Action: Save the guide and extract its preflight checklist. If testing later, use a disposable machine and stop before any storage or authentication change until backups, the disk passphrase, a second key, and recovery media are verified.
- Urgency: This week
- Importance: ★★★★★
- Verified active: November 22, 2026
- Deadline: None
- Cost: Guide and Fedora software are free; compatible FIDO2 keys and test hardware are separate purchases, with no verified regular price stated
- Requirements: Fedora Linux 45 test system; two compatible FIDO2 keys; encrypted LUKS2 storage for the disk-unlock portion; retained passwords, backups, and recovery media
- Official guide: Fedora Linux 45 FIDO2 Lab Guide

2. Use GitHub’s narrower security-advisory roles when Enterprise repositories need help
GitHub organizations on plans that support custom repository roles can now grant four separate permissions for security advisories and private vulnerability reports: viewing; creating and managing; accepting and closing reports; and publishing advisories or requesting CVEs. Merging from a temporary private fork still requires an administrator or security manager.
- Action: Save the permission model as a least-privilege pattern. For any future organization repository, assign only the advisory capabilities a maintainer needs rather than repository administration.
- Urgency: No deadline
- Importance: ★★★★☆
- Verified active: November 22, 2026
- Deadline: None
- Cost: Included only with GitHub organization plans that support custom repository roles; no standalone price is stated
- Requirements: Organization-owner access and a qualifying GitHub plan, including GitHub Enterprise Cloud
- Official announcement: GitHub Changelog
Linux & Self-Hosting
The Fedora lab’s strongest lesson is procedural: authentication changes need independent recovery paths and observable success checks at every layer. Disk unlock, desktop login, privilege elevation, and SSH are separate systems even when the same physical key participates in all four.
GitHub Discoveries
GitHub’s new advisory permissions close a longstanding least-privilege gap. A contributor can now help triage or prepare a private vulnerability disclosure without receiving broad repository administration, while publication and CVE requests can remain separately controlled.
Teaching Corner
Authentication Is a Chain of Fallbacks turns the Fedora lab into a safe paper exercise: students map primary authentication, fallback credentials, recovery assets, and lockout risks without changing a real computer.
PKb Candidates
Authentication-path inventory: For every login or unlock path, record the authenticator, fallback, recovery asset, observable success check, and revocation procedure.
Privilege decomposition: Treat viewing, triage, remediation, acceptance, publication, and deletion as separate capabilities rather than one administrator role.
tags: fedora - fido2 - cybersecurity - github - open-source - linux - teaching